A hacker outsourced break-ins to AI teams and hit 100 companies
The hacker gave short orders like "go crazy," then left the software to test and break into sites for hours.
 Reuters World News · Macron's twilight, Trump's approval and AI hacking
A Chinese-speaking hacker recently broke into the websites of more than 100 companies while doing almost none of the hacking.
Cybersecurity researcher Snor Fagerland watched the spree unfold over a stretch of weeks. The hacker had set up a copy of Cairn, an open-source program that lets teams of AI agents work together toward a shared goal.
An AI agent is software that can take an order and then act on its own, clicking through tools and web pages the way a person would. Cairn links several of those agents together, so they can divide up a job and compare notes. The tool is popular with security testers, known in the industry as red teamers, and with hackers.
In this case, the hacker simply pointed the agents at a target and gave a short order, along the lines of go crazy and hack these guys. The agents then spent hours probing the sites by themselves, testing for weak spots and trying ways inside.
That autonomy is the change. Some of the break-ins were sophisticated enough that a human would have needed lateral thinking and creativity, meaning the ability to spot an odd clue and invent a workaround. Now the hacker could walk away and wait.
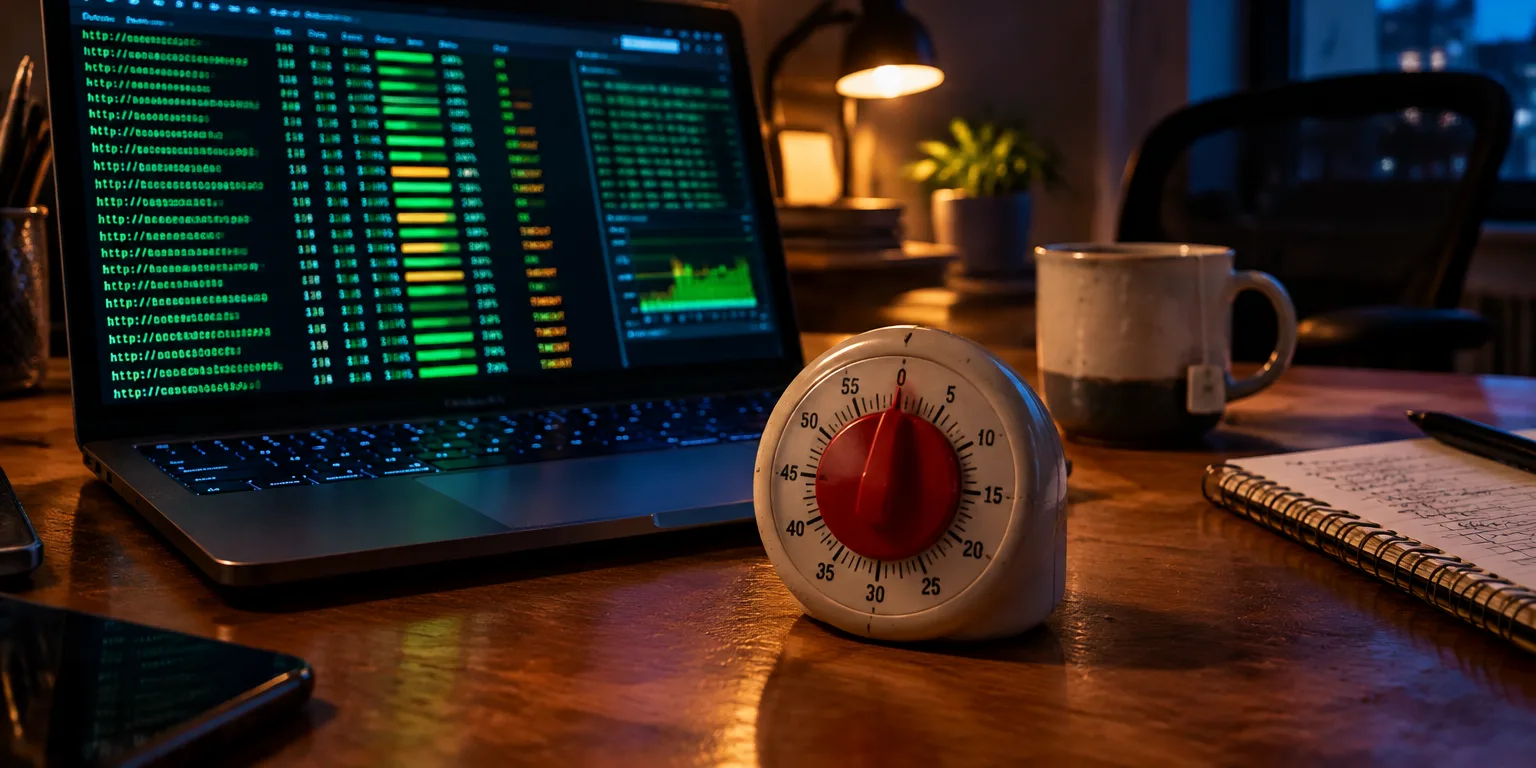
Raphael Satter, who spoke with the researcher, compared it to setting a kitchen timer. You come back when it dings, and something has been hacked.
Cairn's creator says it was not built to carry out attacks. It is not clear how much data, if any, was taken from the more than 100 victims. But the broader effect is that rare skill is no longer required, and that points to a far more dangerous internet.
Questions people ask
What exactly is an AI agent?
An AI agent is software built on a large language model that can use tools, such as a web browser or code interpreter, to complete a task in steps. You give it a goal, and it decides what to try next, checks the result, and keeps going without needing approval for every click.
Is using Cairn illegal?
Cairn itself is open-source software, which means its code is public and anyone can use it. Using it to test your own systems with permission is legal security work, but pointing it at someone else's website to break in is unauthorized hacking under computer crime laws in most countries.
How can a company defend against this kind of automated hacking?
The basic defenses have not changed, but they matter more. Companies are urged to keep software patched, require phishing-resistant logins, limit what each account can reach, and monitor logs for long, automated probing that can signal an agent at work.